Kroemtech

OT security and industrial connectivity

Scymac NetSight

IT/OT Network Monitor

Know what is happening across your IT/OT network

Discover connected devices, understand how IT and OT systems communicate, detect suspicious activity, and focus your team on the security risks that matter most.

Know what is connected.
Know what changed.
Know what needs action.
See How NetSight Works

Features

All you need to see and protect your plant network, in a single appliance

Automatic inventory for OT, IT and IoT

Automatic inventory for OT, IT and IoT

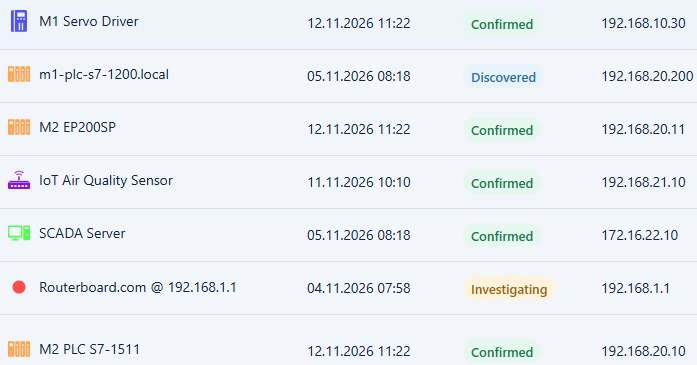
Automatically discover and identify every device communicating on your network – industrial controllers, IoT devices, servers, workstations and network equipment – in one platform for OT and IT. Build and maintain an up-to-date asset inventory without active scanning or manual configuration, and see the risks that cross the line between office and production network.

Automatic inventory for OT, IT and IoT

Passive and safe for production

Passive and safe for production

Monitor network communications without sending requests to connected devices or interfering with running processes. Passive monitoring makes NetSight suitable for sensitive industrial environments where stability, availability, and uninterrupted operation are essential.

Passive and safe for production

Network map, zones and connections

Network map, zones and connections

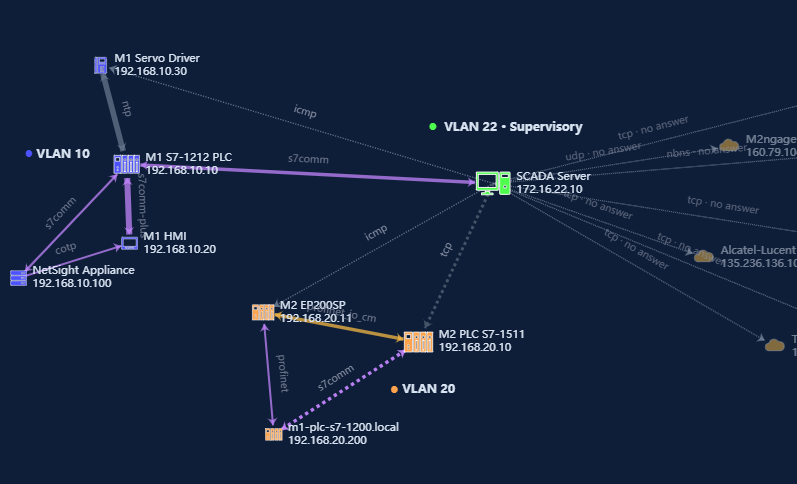
Visualize your network topology, connected devices and communication paths in an interactive network map. Organize assets into logical zones to understand segmentation, and learn which connections are normal for your plant, so that new or unexpected connections stand out at a glance.

Network map, zones and connections

Alerts on network changes

Alerts on network changes

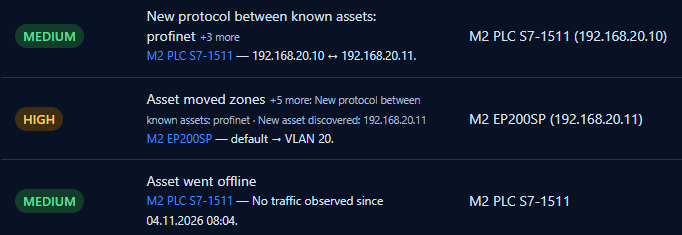
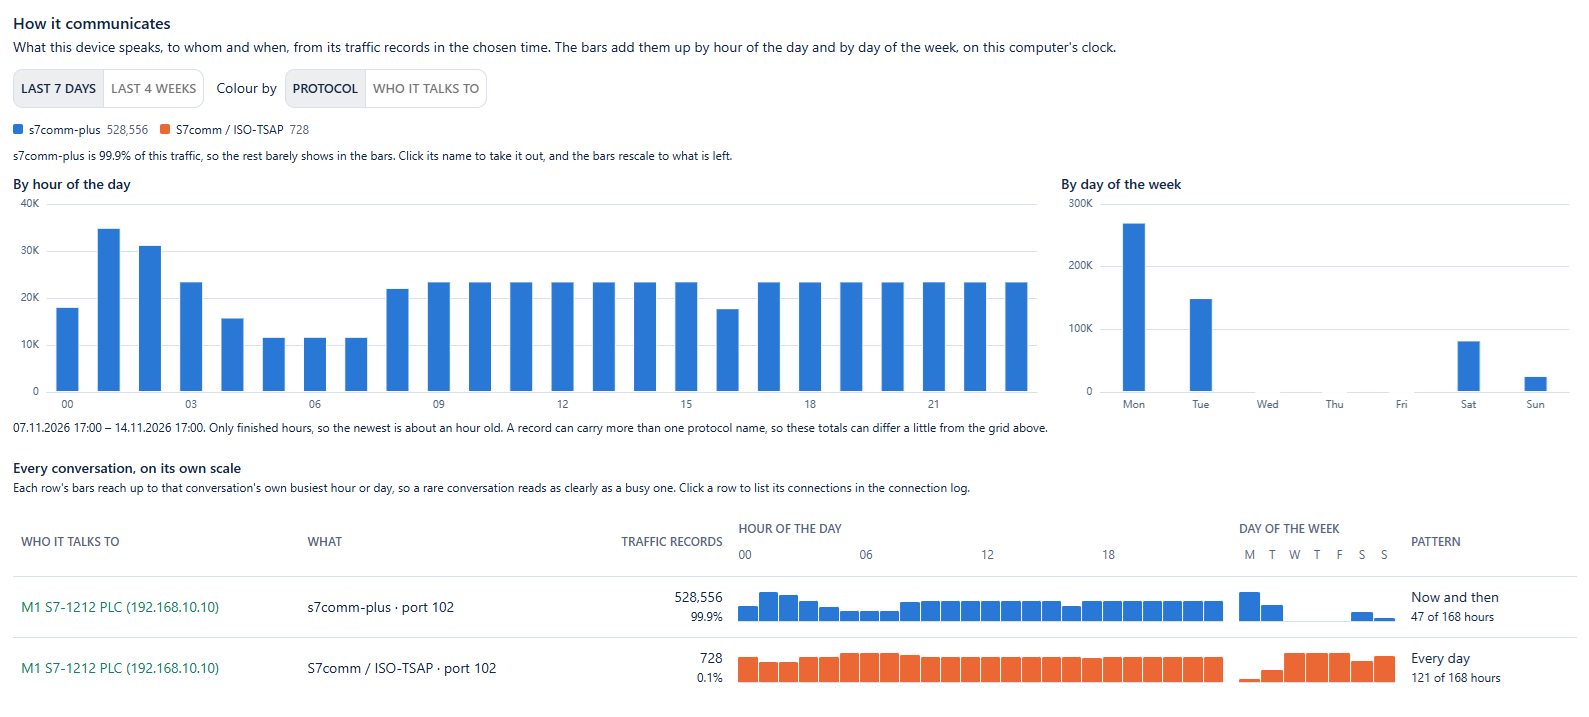
Be notified when something changes in your network: a new device appears, a device starts communicating with new partners, or traffic deviates from its usual pattern. Your team sees what changed and when, and can check whether the change was planned before it turns into a problem.

Alerts on network changes

Risk and vulnerability management

Risk and vulnerability management

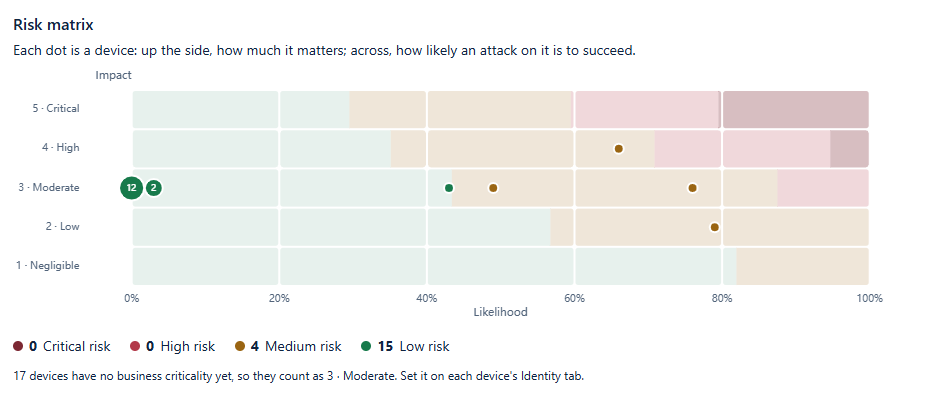
Identify potential vulnerabilities and security risks across your IT and OT networks. Assess and prioritize threats based on their likelihood, potential impact, and business relevance. Gain a clear understanding of your security posture, track identified risks, and focus remediation efforts where they matter most.

Risk and vulnerability management

Document incidents, meet NIS2 deadlines

Document incidents, meet NIS2 deadlines

Record each security incident with the devices, alerts and vulnerabilities involved, the evidence, and a timeline that can’t be edited afterwards. When an incident is significant under NIS2, NetSight counts down the 24-hour, 72-hour and one-month deadlines, reminds you before each one, and drafts the early warning, the incident notification and the final report from what you recorded, ready to check and file on the authority’s portal.

Document incidents, meet NIS2 deadlines

Audit-ready reports

Audit-ready reports

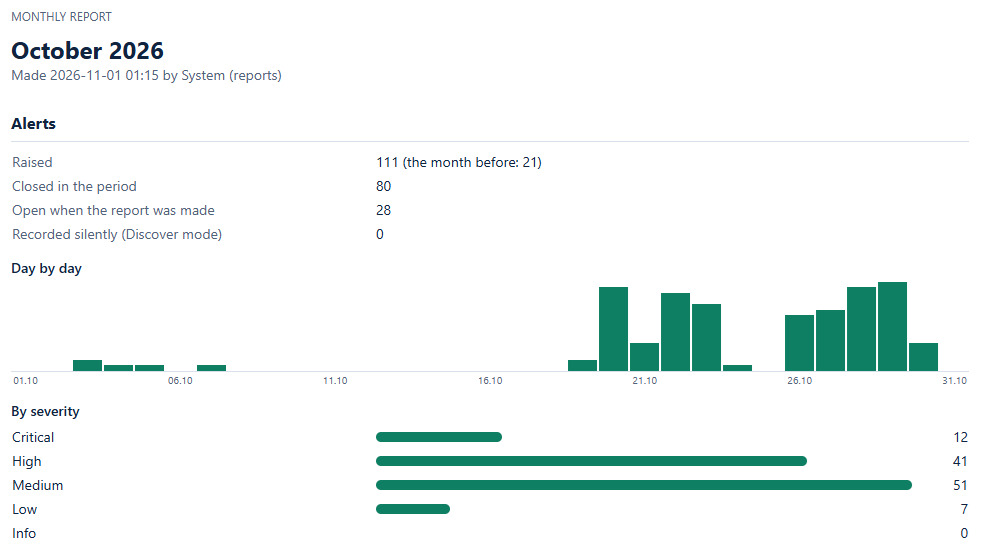
Turn network activity, discovered assets, vulnerabilities, and security events into clear, structured reports. Support internal security reviews, compliance assessments, and management decisions with documented evidence of your network's security posture.

Audit-ready reports

Runs entirely on site

Runs entirely on site

Deploy NetSight directly within your own infrastructure and maintain control over your sensitive network information. Local processing and storage keep monitoring independent of external cloud services, supporting data sovereignty and the security requirements of critical environments.

Runs entirely on site

Scymac NetSight

How It Works

01

Connect & Monitor

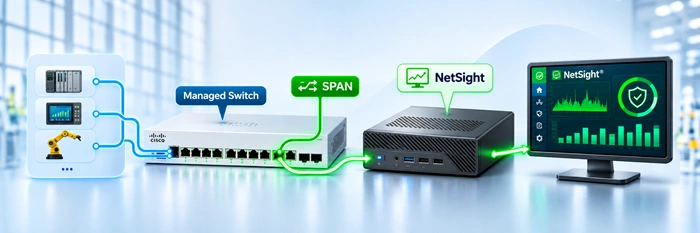
Deploy NetSight within your industrial network by connecting it to the SPAN port of a managed switch. It passively analyses network traffic without interfering with production processes or equipment.

02

Discover & Map

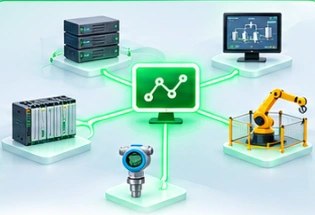
Automatically identify connected devices, industrial protocols and communication patterns. Build a continuously updated inventory and understand how your systems interact.

03

Detect & Assess

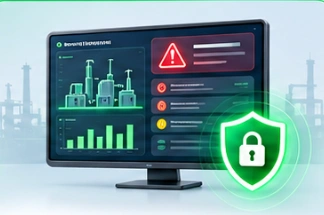
Identify unusual network activity, potential intrusions, known vulnerabilities and security weaknesses before they escalate into costly incidents.

04

Prioritize & Act

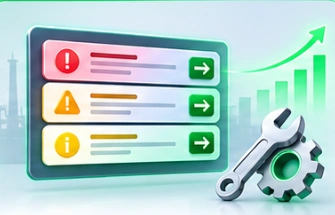
Turn technical findings into actionable insights. Focus maintenance and security efforts on the risks that matter most to operational continuity.

Built for SMEs

The IT/OT monitoring solution for industrial SMEs

Gain complete visibility and stronger cybersecurity for your production and business networks – without the complexity and cost of enterprise tools.

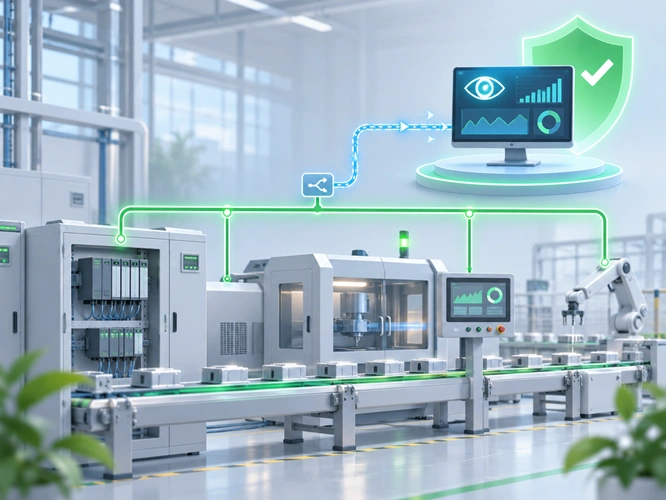
Factory protected by a security shield

Easy deployment

Get up and running quickly in your existing IT and OT environment.

All-in-one solution

Asset discovery, network monitoring, threat detection and vulnerability insights in a single, easy-to-use platform.

Independent operation

Runs locally and without cloud dependency – ideal for industrial environments.

Cost-effective security

Focus on the risks that matter, with comprehensive protection tailored to the needs and budget of SMEs.

The bigger picture

From network traffic to management decisions

Turn network data into clear, actionable insights. NetSight combines visibility, asset context and security analysis, so you always know what you have, what’s happening, and what to do next.

  • Complete visibility

    See devices, communications and relevant activity across your IT and OT networks.

  • Turn insight into context

    Enrich network data with asset, vulnerability and risk information.

  • Act with confidence

    Prioritize, investigate and take the right measures based on business impact.

Network traffic

What we see

Analysis & context

What it becomes

Management decisions

What you can do

Know what you own

Devices

Curated asset inventory

Know what is normal

Communications

Flows and topology

Know what changed

Changes

Actionable alerts

Know what needs investigation

Security detections

Security events

Know what may be exposed

Product + firmware

Vulnerability findings

Know what is most urgent

KEV + EPSS + CVSS

Prioritization

Know where risk is concentrated

Asset criticality + exposure

Risk zones

Know what is being done

Handling decisions

Ownership and history

Risk-based prioritization

Prioritize the risks that matter most

Not every vulnerability deserves the same response. NetSight combines technical findings with operational context so your team can focus on the assets and exposures that would have the greatest impact on production, safety, and business continuity.

Risk scores combine impact and likelihood using factors such as:

  • Business criticality
  • Safety relevance
  • CVSS
  • EPSS
  • Known exploited
  • Lifecycle status
  • OT protocol exposure
  • External reachability
  • Zone bridging
  • Open alerts

Adjust the weighting to match your environment and decision-making priorities.

Why this matters

The goal is not another score. It is to show where the next hour or euro of security work will reduce risk the most.

Asset risk snapshot

Overall risk

HIGH

Main risk drivers

  • Critical production asset

  • Known exploited vulnerability

  • End of support

  • Cross-zone communication

Recommended actions

  • Apply vendor mitigation

  • Restrict cross-zone access

  • Review accepted-risk decision

Network visibility

The hidden risks of an outdated OT network diagram

A network diagram is only as reliable as the information behind it.

When network documentation no longer reflects reality, even small discrepancies can have serious consequences. Unknown connections, overlooked devices and incorrect assumptions about network segmentation can undermine security, delay investigations and complicate compliance.

The problem isn’t just an inaccurate diagram. It’s the decisions made based on incomplete information.

  • Hidden security risks

    Undocumented devices and communication paths can create blind spots, leaving vulnerabilities and unwanted connections unnoticed.

  • Slower incident response

    Without a reliable network overview, identifying affected systems, tracing communications and understanding the impact of an incident takes longer.

  • False sense of security

    Outdated documentation can create misplaced confidence in network segmentation, security controls and compliance readiness.

Replace assumptions with visibility.

Scymac NetSight continuously observes network communications, helping you validate your documentation, identify unexpected changes and make informed decisions based on what is actually happening in your IT/OT network.

Compliance

Evidence for NIS2, IEC 62443 and the ICT Minimum Standard

Regulations and standards keep asking the same questions: What do you operate? What has changed? Which weaknesses are open, and who is handling them? How did you respond to an incident? NetSight answers them from your own network and keeps the evidence.

NIS2

EU directive for essential and important entities, including many manufacturers.

What it asks for

Risk management measures such as asset management, vulnerability handling and incident handling, and the reporting of significant incidents within 24 hours, 72 hours and one month.

What NetSight provides

  • An up-to-date asset inventory
  • Vulnerability decisions with owners and history
  • Incident records with a complete timeline

IEC 62443

International standard series for industrial automation and control systems.

What it asks for

Zones and conduits, continuous monitoring of the control network, and a managed process for patches and vulnerabilities.

What NetSight provides

  • Zones with Purdue levels, address ranges and VLANs
  • Detection of communication that bridges zones
  • Patch, mitigation and accepted-risk decisions

Switzerland: ISG and ICT Minimum Standard

Information Security Act and the federal guideline for critical infrastructure.

What it asks for

Operators of critical infrastructure must report cyberattacks to the Federal Office for Cybersecurity within 24 hours. The ICT Minimum Standard structures protection along Identify, Protect, Detect, Respond and Recover.

What NetSight provides

  • Identify: asset inventory and vulnerabilities
  • Detect: alerts on changes in the network
  • Respond: documented incidents for the report

NetSight provides the technical evidence. It does not replace your management system or a formal assessment – that is where our partner SCMC comes in.

See the partnership

Technical data

Scymac NetSight at a glance

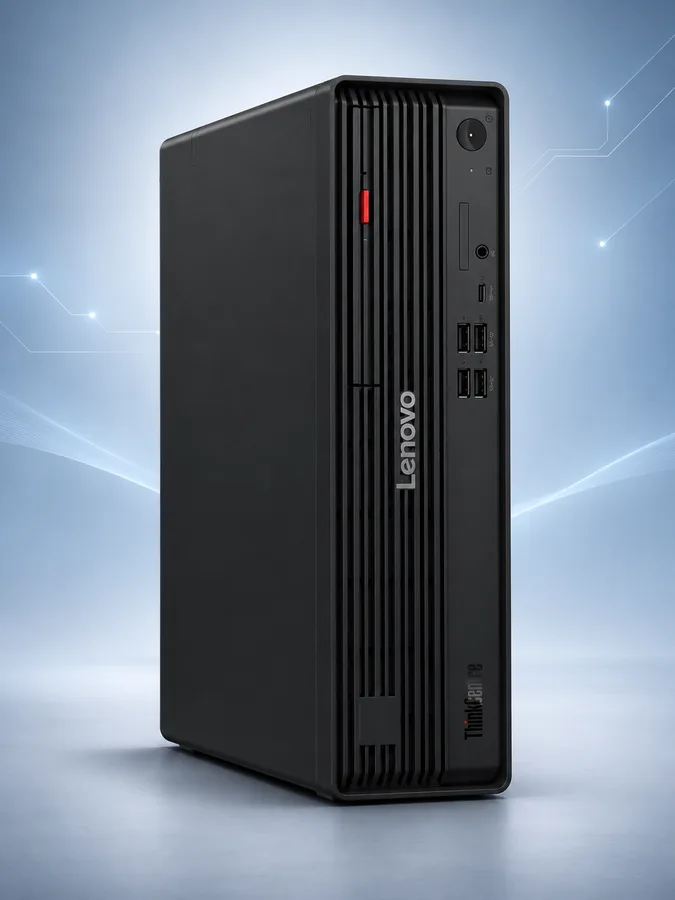
Scymac NetSight appliance
Delivery
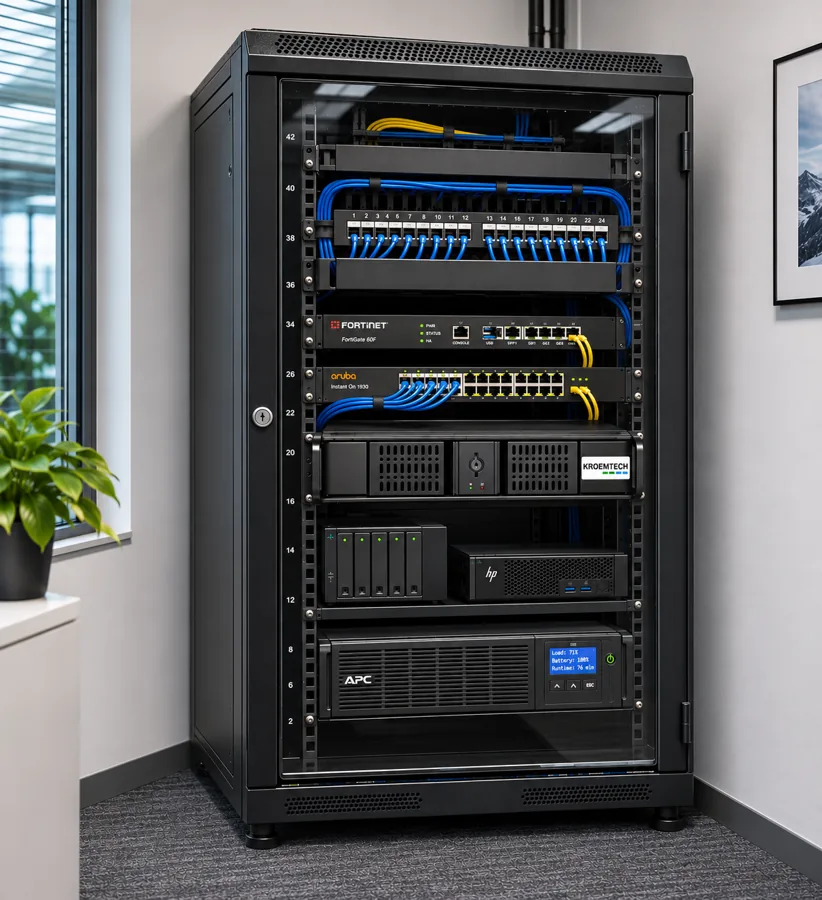
Pre-configured appliance, installed on site
Mirror port
1 port for the switch’s mirror (SPAN) copy. Receive only: no address, nothing sent, and the appliance counts it as proof
Probe port (optional)
A second port that asks single devices for their identity: one device per request, never a broadcast, only by users allowed to
User interface
In the browser, served by the appliance over HTTPS; English, German and Portuguese
SCMC

Partner

From plant security to management reporting, with SCMC

KROEMTECH works with SCMC, the Swiss Cybersecurity Management Center: a Swiss platform for structured cybersecurity self-assessments against the ICT Minimum Standard, ISO 27001 or NIST CSF 2.0, with data stored in Switzerland.

What NetSight shows in your plant – the inventory, open vulnerabilities and the measures you decide on – can be recorded in SCMC as measures and tracked in your maturity level. Management sees where the company stands and what is still open.

More about our partnershipwww.scmc.ch

FAQ

Commonly asked questions

No, not by default. It listens to a copy of your traffic from a mirror (SPAN) port and never transmits on it. The only feature that sends packets is optional active identification: one device at a time, through a separate probe port, never broadcast, with a cooldown per device, and only for users an admin has given probe permission.

No. Everything is analysed on the appliance. In air-gapped mode it makes no outbound connections. Vulnerability catalogues, threat lists and software updates can all be uploaded as signed files through the offline browser interface. When internet access is allowed, it only downloads updates or public catalogues (NVD, CISA, FIRST and the threat lists) directly from our secure Swiss-hosted server, and you can switch that off at any time.

Your traffic, asset inventory and all security decisions remain stored locally on the appliance, on site. If online mode is enabled, Scymac NetSight can use anonymized product names and version information to query our server for lifecycle information. No network traffic, asset inventory or operational data is transmitted. These lookups are optional and can be disabled at any time. In air-gapped mode, no external lookups are performed.

The appliance comes pre-configured and ready to deploy. Simply connect the monitoring interface to a mirror or SPAN port on the switches you want to observe. Your team can then access Scymac NetSight through its browser-based interface, hosted directly on the appliance itself. A second network interface connected to the plant network is only required if you choose to enable active device identification.

It recognises the common OT protocols, including Modbus/TCP, S7comm, EtherNet/IP (CIP), DNP3, BACnet and PROFINET, as well as layer-2 traffic such as LLDP and spanning tree. Active identification supports PROFINET DCP, EtherNet/IP, S7comm, BACnet and SNMP.

Devices start appearing within minutes. A new installation starts in Discover mode, which records alerts silently while the inventory fills, so your team can review and confirm devices before switching on alerting.

Yes. It identifies each device's manufacturer, model and firmware from its traffic, then matches them against NVD, CISA ICS advisories, CISA's Known Exploited Vulnerabilities list and FIRST EPSS. Users can also enter this information manually. Every match shows why it was made and how confident it is. Optional active identification (probing) can read the exact firmware version, which allows exact matching.

Yes. That is the normal case in OT, and the workflow is built for it. You can record a compensating control, schedule a patch for the next shutdown, or accept the risk until a review date, each with an owner and a note. The system reopens the decision when the firmware changes, when the CVE starts being exploited in the wild (CISA KEV), or when the acceptance expires.

Risk = Impact × Likelihood. Impact comes from the device's business criticality and safety relevance. Likelihood comes from its vulnerabilities, open security alerts, vendor support status, exposed OT protocols, internet contact and zone bridging. Each device page explains its own score, and an admin can adjust the weights.

Alerts can be sent to your SIEM over syslog (RFC 5424) and by email, each with its own severity threshold. The inventory can also be exported. Custom connectors are also possible.

Yes. The inventory is organised by site, zone and collector, and each collector's health is checked. Zones carry Purdue levels, address ranges and VLANs.

There are three roles. Viewers can read everything. Technicians can curate the inventory and handle alerts and vulnerabilities. Admins manage users, zones, settings, updates and backups. The server enforces these limits, not just the interface. Every change, sign-in and refused request is written to an audit log.

Everything your team decided can be backed up and restored on a new appliance: device names and states, zones, accepted zone bridges, and vulnerability decisions with their full history. Traffic-derived data is rebuilt by the next scans.

Unlike complex enterprise solutions, NetSight is designed for industrial SMEs that need cost-effective IT/OT visibility and cybersecurity without a dedicated security team.

It combines passive network monitoring, asset discovery, transparent risk scoring, vulnerability management and NIS2 incident reporting in a single, easy-to-use appliance.

Fully on-premises and offline-capable, NetSight keeps sensitive network data under your control while helping small teams identify risks, prioritize actions and protect production without disrupting operations.

You do not need more security data. You need a clear picture of your risk.

Scymac NetSight brings asset visibility, network monitoring, intrusion detection, vulnerability management and OT risk into one local platform.

See what is connected.

Understand what changed.

Prioritize what matters.